TechSonar, DevSecOps, AppSec & Platform Security Consultancy
TechSonar embeds senior security engineers directly into your organisation. We deliver AppSec (SAST, DAST, SCA), CVE triage and enrichment, threat modelling, risk-led security programmes, and continuous compliance across SOC2, ISO 27001, DORA, and GDPR, not as a one-off engagement, but as an ongoing, embedded capability that keeps your security posture strong every day of the year.
Why TechSonar
Highly qualified engineers. Meaningful impact. Every day.
security engagements
Compliance programmes, AppSec assessments, threat modelling, and continuous DevSecOps engagements delivered across regulated industries.
SENIOR ENGINEERS
Every engagement is led and delivered by senior security engineers. No juniors, no automated-only tooling, no box-ticking reports that gather dust.
days a year
Continuous, embedded security coverage, not point-in-time audits. We stay active so your posture never lapses between compliance windows.
Trusted by




What we do
Impactful security across every layer of your stack
From AppSec and CVE triage to continuous compliance, threat modelling, IaC security, and cloud platform engineering, TechSonar delivers security that makes a real difference. Embedded, continuous, and led by senior engineers who understand both security and how modern software is built.
[01]
Find what matters. Fix it before it ships.
Automated scanners produce noise. Our engineers produce signal. We integrate SAST, DAST, and SCA directly into your CI/CD pipelines and then do the work that tools cannot, triaging and enriching every CVE with business context so your teams know exactly what to fix, in what order, and why.
 SAST, DAST, and SCA embedded into CI/CD, not bolted on after the fact.
- CVE triage and enrichment driven by business context, not just CVSS scores.
- Business-logic vulnerability identification that automated scanners miss entirely.
- Dependency and supply chain security across your full stack.
- Findings that come with remediation guidance, not just a report.

Why TechSonar is different
Most security engagements end when the report is delivered. TechSonar engineers stay embedded, working alongside your team to ensure findings are remediated, controls are maintained, and your security posture improves continuously. Not fix-and-forget. Not point-in-time. Every day.
Continuous
Security coverage every day of the year, not just at audit time.
Expert-led
Senior engineers only. No juniors, no automated-only outputs.
Embedded
Part of your team, not an external vendor dropping in once a year.
Risk-led
Prioritised by real risk to your business, not generic compliance checklists.
Our capabilities
Security that goes deeper than the audit.
TechSonar engineers are embedded into your organisation, delivering meaningful, impactful security across AppSec, compliance, threat modelling, IaC, and cloud platform engineering. Not box-ticking. Not fix-and-forget. Real security, every day of the year.
[AppSec]
Application Security
SAST · DAST · SCA · CVE Triage
- SAST, DAST, and SCA integrated into your CI/CD pipelines
- CVE triage and enrichment, context-driven, not just CVSS scores
- Supply chain and dependency security across your full stack
- Business-logic vulnerabilities that automated scanners miss
[Compliance]
Compliance & Continuous Compliance
SOC2 · ISO 27001 · DORA · GDPR
- SOC2 Type I/II and ISO 27001:2022 readiness and certification
- DORA: ICT risk management, incident response, third-party oversight
- GDPR: data protection by design and technical control implementation
- Continuous control monitoring, evidence collected daily, not pre-audit
[Architecture]
Threat Modelling & Architecture
Risk-led · Embedded · Continuous
- Threat modelling for features, services, and infrastructure changes
- Security architecture review and zero-trust design
- Risk-led programmes tailored to your actual threat landscape
- Security embedded into your engineering and design process
[DevSecOps]
Continuous DevSecOps
Embedded · Ongoing · Year-round
- Senior engineers embedded in your sprints and standups
- Continuous monitoring, drift detection, and rapid remediation
- Security reporting that gives leadership real visibility
- Security culture built into your engineering practice
[IaC]
IaC & Pipeline Security
Terraform · Pulumi · CloudFormation
- IaC security for Terraform, Pulumi, CloudFormation, and Ansible
- Policy-as-code enforcement with OPA, Checkov, and custom rulesets
- Pipeline hardening: secrets management and supply chain controls
- Pre-merge security gates that stop misconfigurations at source
[Cloud]
Cloud & Platform Engineering
AWS · Azure · GCP · Kubernetes
- Secure cloud architecture design across AWS, Azure, and GCP
- Identity and access management: least-privilege and RBAC
- Network segmentation, micro-segmentation, and zero-trust access
- Kubernetes and container security: image scanning and runtime protection
Capabilities
Deep expertise across the full security stack
From SAST/DAST/SCA and CVE triage to threat modelling, DORA, GDPR, continuous compliance, and embedded DevSecOps, these are the capabilities TechSonar brings to every engagement. Delivered by senior engineers, embedded into your organisation, active every day of the year.
SAST / DAST / SCA
We integrate Static Analysis, Dynamic Analysis, and Software Composition Analysis directly into your CI/CD pipelines, so every commit is validated before it reaches production. No bolt-on scanning, no ignored reports. Findings come with context and remediation guidance.
CVE Triage & Enrichment
We do not just surface CVEs, we triage and enrich them with business context. Our engineers cut through scanner noise to identify which vulnerabilities pose real risk to your organisation, so your teams fix what matters and do not waste cycles on theoretical issues.
Threat Modelling
We embed threat modelling into your engineering process, reviewing new features, services, and infrastructure changes before they ship. Security designed in, not discovered after launch. Attack surface analysis, trust boundary mapping, and risk-prioritised findings.
Risk-Led Security Programmes
We build security programmes around your actual threat landscape, not generic frameworks. Every control, every policy, every process is prioritised by the risk it mitigates for your specific organisation, not because a checklist says so.
SOC2 & ISO 27001
From gap analysis to certification, and beyond. We implement controls, build audit-ready evidence, and stay embedded to ensure your compliance posture never lapses between audit windows. Continuous compliance, not annual scrambles.
DORA Compliance
We help financial services organisations meet Digital Operational Resilience Act requirements, ICT risk management frameworks, incident response and reporting procedures, third-party risk oversight, and digital resilience testing embedded in your DevSecOps practice.
GDPR & Data Protection
We implement data protection by design across your infrastructure and pipelines, privacy impact assessments, technical controls for data minimisation and access restriction, and engineering-level GDPR compliance that goes beyond policy documents.
Continuous Monitoring
Security is not a point-in-time activity. We provide continuous monitoring of your controls, pipelines, and infrastructure, detecting drift and responding before it becomes a finding or a breach. Every day, not just before the next audit.
Pipeline & IaC Security
We harden your CI/CD pipelines and secure your Infrastructure as Code, Terraform, Pulumi, CloudFormation, and Ansible, against misconfigurations and policy violations before they reach any environment. Policy-as-code enforcement with OPA, Checkov, and custom rulesets.
Cloud Platform Security
We design and implement secure cloud architectures across AWS, Azure, and GCP, covering identity and access management, network segmentation, workload protection, Kubernetes security, and cloud-native security controls. Security built in from day one.
Embedded DevSecOps
Our engineers work as part of your team, not as external consultants who drop in once a year. We integrate into your sprints, your standups, and your delivery process to keep security moving at engineering speed. Embedded, not adjacent.
Map every asset. Secure every change.
SecureOps AI agents map your entire attack surface and test it daily with expert-level precision.
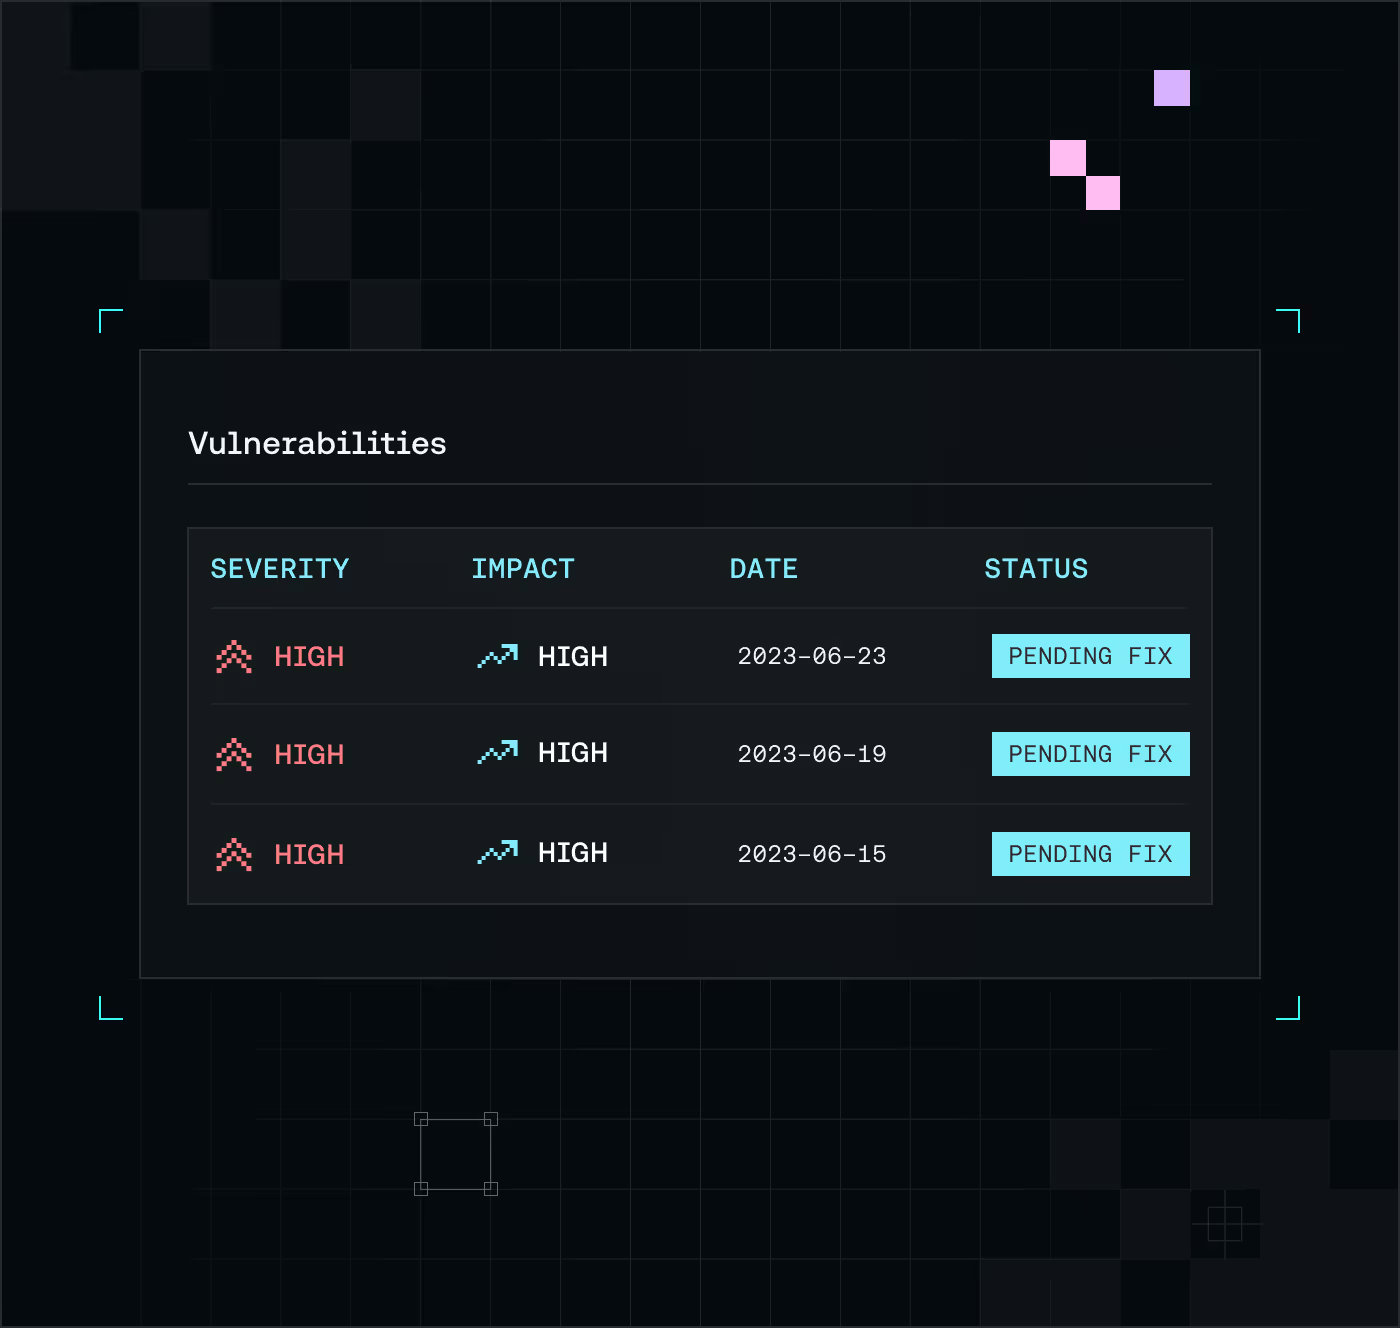
Map your assets and detect exposures.
Continuously discover infrastructure, pipelines, and new exposures before they become real risks.
Secure every day, with expert precision.
AI-driven security assessments adapt to every change in your infrastructure and applications, replicating top security experts at machine speed.
Remediate smarter, right at the code.
Accelerate remediation with offensive context, actionable guidance, and continuous validation of results.
Compliance
Engineering-led compliance across every major framework
We specialise in SOC2 and ISO 27001, and support the full range of compliance frameworks your business needs to operate in regulated markets.
Our DevSecOps Accelerator programme takes you from gap analysis to SOC2 Type I or Type II certification, with security controls embedded directly into your engineering practice.
- Gap analysis and control mapping
- Pipeline and IaC control implementation
- Audit-ready evidence and documentation
We implement and maintain your ISMS aligned to ISO 27001:2022. From risk assessments and policy management to control implementation and internal audits.
- ISMS design and implementation
- Risk assessment and treatment
- Policy and procedure development
Meet Digital Operational Resilience Act requirements with ICT risk management frameworks, incident response procedures, and third-party oversight embedded in your DevSecOps practice.
- ICT risk management framework
- Incident response and reporting
- Third-party risk oversight
Ensure data protection by design across your infrastructure and pipelines. We help you implement technical controls that satisfy GDPR requirements at the engineering level.
- Data protection by design
- Technical control implementation
- Privacy impact assessments
Protect patient data with security controls, access management, and audit trails aligned to HIPAA Security Rule requirements, built into your DevSecOps workflows.
- PHI protection controls
- Access management and audit trails
- Security risk analysis
Secure cardholder data environments with continuous vulnerability management, network segmentation validation, and compliance controls embedded in your pipelines.
- Cardholder data environment security
- Network segmentation validation
- Continuous vulnerability management
Industries
TechSonar operates where compliance pressure is highest
Targeted DevSecOps expertise. Industry by industry.
Finance
Protecting financial platforms with AI-led security assessment and expert DevSecOps engineering.
FinTech
Securing payment systems, APIs, and cloud-native architectures for fast-moving fintech companies.
Technology
Securing innovation with AI-led security assessment and expert security teams.
Telecom
Protecting networks, platforms, and millions of subscribers.
Energy
Safeguarding critical infrastructure from advanced threats.
Healthcare
Protecting patient data and critical systems with AI-led security and HIPAA compliance.
SaaS
End-to-end DevSecOps for SaaS products from development to production.
Manufacturing
Protecting production lines and digital supply chains.
Testimonial
Trusted by engineering teams that take security seriously
"TechSonar was exceptional when addressing our sense of urgency with regards to an important compliance timeline, and they were able to deliver effectively, implementing critical security controls across our infrastructure."
Banking · Client Review
Third-Party Proof
Recognized by the industry.
Backed by results.
From independent evaluations and analyst reports to awards and client recognition, see how SecureOps is earning trust across the cybersecurity ecosystem.
SecureOps selected as a 2026 Cyber150 winner by IT-Harvest
SecureOps has been named a 2026 Cyber 150 winner by IT-Harvest, recognizing its growth, innovation, and contribution to the future of cybersecurity through continuous security validation.
SecureOps recognized as a Challenger / Fast Mover in the GigaOm Radar for 2025
We're proud to share that SecureOps has been recognized as a Challenger and Fast Mover in the Innovation/Feature quadrant of the latest GigaOm Radar.
SecureOps now on Gartner Peer Insights
By joining Gartner Peer Insights, SecureOps is opening a new space for transparency, where clients can share how continuous security validation and AI-driven DevSecOps help them stay one step ahead.
SecureOps featured in Forbes: Leading the next chapter of cybersecurity innovation
Forbes features SecureOps's founder on its cover, a story of bold leadership, innovation, and how SecureOps is redefining DevSecOps through AI and global growth.
By the numbers
Clients secured
Across regulated industries globally
Frameworks mapped
ISO 27001 · SOC 2 · NIST · PCI-DSS · NIS2 · CIS · DORA · GDPR · HIPAA · OWASP · MITRE ATT&CK · EU AI Act
Programmes delivered
Accelerator, IaC, Security Focus, Bespoke & more
Why clients trust us
Senior engineers only
No juniors. No box-ticking.
Continuous coverage
365 days, not point-in-time audits.
Auditor-aligned delivery
Evidence-ready. No unnecessary work.
Rapid time-to-value
Embedded within days, not months.
Press & coverage
What the industry is saying.
"TechSonar's embedded model is closing the gap between compliance theatre and real security posture."
"A pragmatic approach to framework alignment that regulated firms are increasingly demanding."
"Cutting through the noise: senior-only delivery and continuous coverage set TechSonar apart."
Stop fixing security once a year. Start doing it every day.
Whether you need to reach SOC2 or ISO 27001 fast, maintain compliance through an audit window, embed AppSec into your pipelines, or build a risk-led security programme from the ground up, TechSonar provides the senior engineering expertise to get you there and keep you there.
Resource Hub
In-depth knowledge of what's happening in the cybersecurity industry
Ebook
Anatomy of a DevSecOps Assessment
See how we turn security findings into clear, actionable insights. This sample report walks you through a complete security assessment, from the executive summary to the technical details of each vulnerability.
Case Study
How a global bank reduced security assessment time from a week to a day and a half.
A major financial institution needed a faster way to run security assessments across teams of varying seniority and a growing attack surface. Find out how SecureOps helped make their security validation more agile.
Event
DevSecOps Summit 2026
The most important DevSecOps event of the year. It will bring together leading industry brands, experts, and strategic partners to present new solutions, share experiences, and address the main challenges in security engineering.